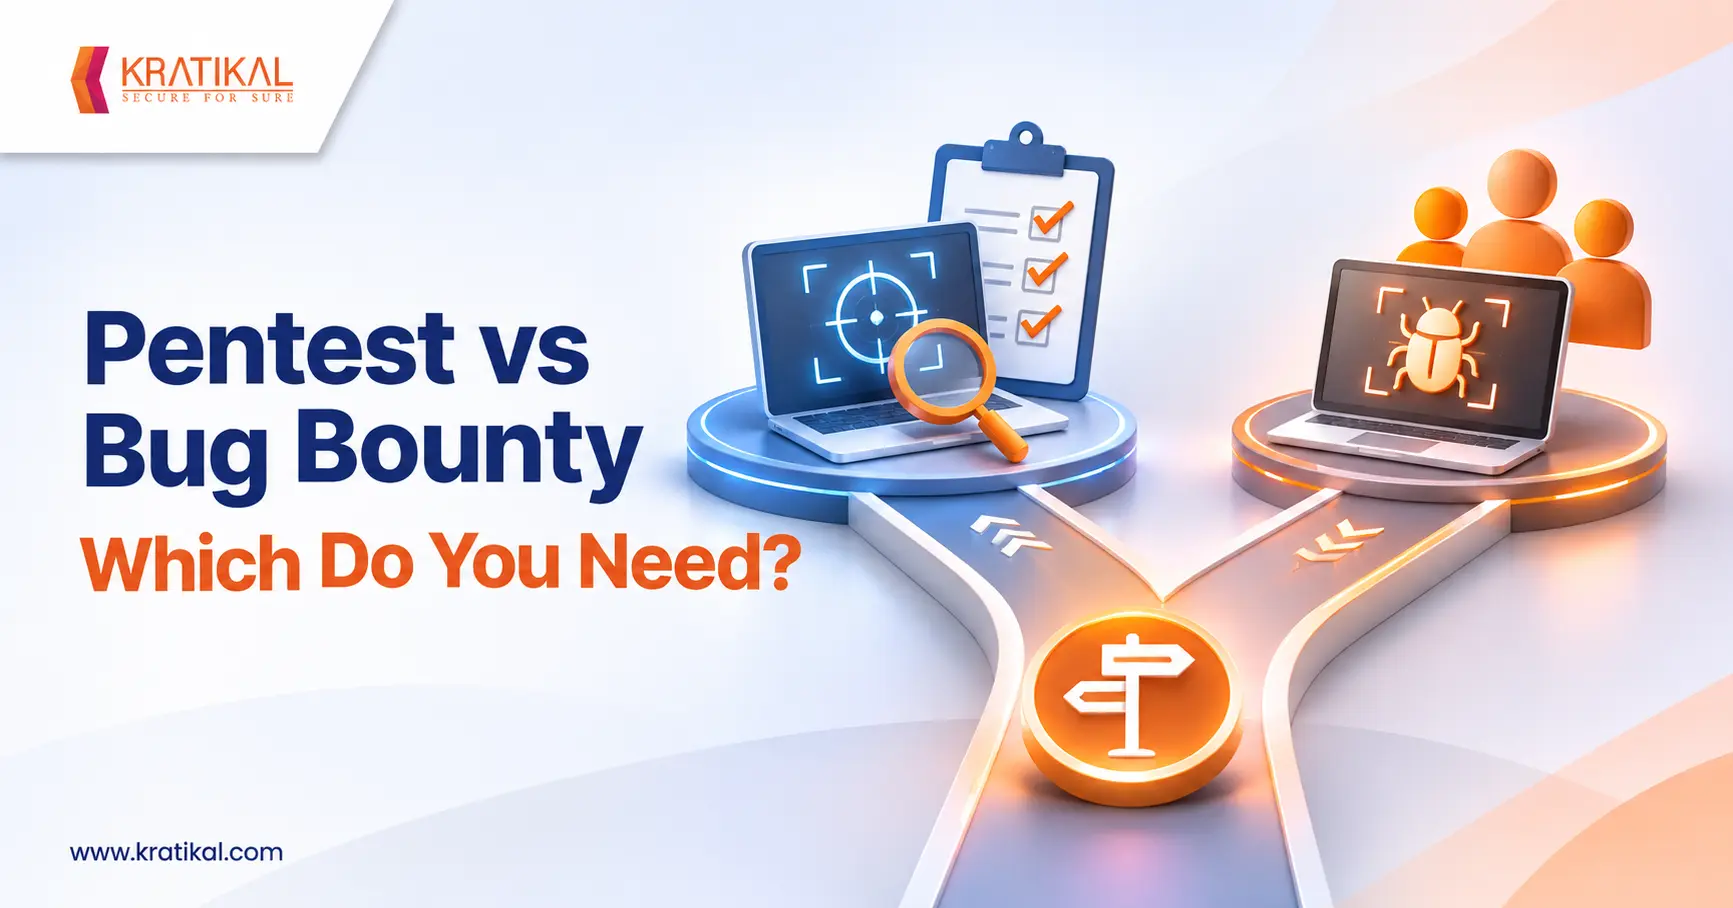
A pentest and a bug bounty answer different questions. In a pentest, a hired team runs a scoped, time-boxed test of defined systems against a set method and produces audit evidence. A bug bounty pays outside researchers for each valid finding, for as long as it runs. Most companies need a pentest first, and a bug bounty later.
People often frame the choice as either one or the other. Bug bounty platforms say crowds find more. Pentest firms say crowds find the wrong things. However, both are selling something. The useful question is simpler: what do you need to know, and by when? This guide on the pentest vs bug bounty choice answers that for each stage of a security programme.
Pentest vs Bug Bounty: The Core Difference
A penetration test is a controlled attack on your systems by a team you hire. The team agrees on a scope, follows a set method, tests every item in that scope within a set window, and delivers a report. You pay for the project, whether the testers find 2 issues or 20.
A bug bounty programme invites outside security researchers to look for vulnerabilities in your systems and pays them for each valid finding they report. The programme can run for months or years. You pay for results, not effort, and you have no guarantee that any particular system gets tested at all.
Think of it as a house. A pentest is a home inspection. The inspector walks through every room on a list, by a set date, and signs a report you can show a buyer or a bank.
A bug bounty is more like a reward poster on the front door: anyone who finds a way in and reports it gets paid. The poster can attract skilled people for years, and some of them will find things the inspector missed. But nobody promises to check the basement.
Bug Bounty vs Pentest Side by Side
The bug bounty vs pentest comparison is clearest on the same criteria.
| Criterion | Pentest | Bug bounty |
| Who tests | A hired team, vetted and named | Outside researchers, often anonymous |
| Scope | Agreed in advance, tested in full | Defined, but researchers choose what to test |
| Coverage | Every item in scope, against a set method | Whatever researchers find most rewarding |
| Duration | Days to weeks | Ongoing, often months or years |
| Cost model | Fixed fee for the engagement | Platform fee plus a payout per valid finding |
| Cost predictability | High | Low; payouts depend on what is found |
| Internal systems | Can be tested | Rarely in scope |
| Business logic and access control | Tested with insider context | Tested without insider context |
| Report | Formal report with methodology and retests | Individual findings, as they arrive |
| Compliance evidence | Yes, for PCI DSS, SOC 2, ISO 27001, CERT-In audits | Rarely accepted on its own |
| Legal footing | Signed contract and rules of engagement | Programme terms and safe harbour |
Overall, neither column wins outright. With a pentest, you get certainty about coverage and a report you can use. A bug bounty gives you a wider pool of skill and time, with no promise about what it covers.
Pentest Coverage: What Each One Actually Tests
Pentest coverage is the main reason auditors and boards prefer it. The testers agree on a scope, then work through it against a published method, such as the OWASP testing guide for web apps. Every user role, every workflow, and every endpoint in scope gets attention, including the routine ones.
A bug bounty, however, works differently. Programmes pay researchers per finding, so they go where findings pay best and come quickest. As a result, popular, internet-facing features get heavy attention. Internal tools, admin panels behind a VPN, and features that need a special account often get none. In the house picture, the reward poster draws plenty of people to the front door and the windows. The basement stays dark.
Access control, for example, shows the difference clearly. Testing whether one user can see another user’s data needs several accounts with different roles, and knowledge of who should see what. In OWASP’s 2025 data, 100% of applications tested had some form of broken access control. A pentest team gets test accounts for every role as part of the engagement. Bug bounty researchers usually test with whatever access a public sign-up gives them.
Coverage is also where a pentest differs from a scan, as this comparison of pentesting and vulnerability scanning explains. Coverage depends on the testing approach too. This guide to box testing techniques explains how black, grey, and white box testing change what testers can reach.
Bug Bounty Limitations
Bug bounties are powerful, but bug bounty limitations are easy to miss until the programme is live. The most common ones are:
- No coverage guarantee. Researchers test what interests them. A system can sit in scope for a year without a serious look.
- Triage load. Public programmes attract duplicates, low-quality reports, and automated scanner output. Someone on your team has to sort every one.
- Unpredictable cost. Payouts depend on what researchers find, so one busy month can exceed a quarterly budget.
- External systems only, in practice. Internal networks, unreleased features, and systems that need special access rarely make it into scope.
- No business context. Researchers do not know your business rules, so logic flaws that look normal from outside can go unreported.
- Legal exposure. Researchers test your live systems. Clear programme terms and safe harbour language are essential, as the Indian section below explains.
- Weak audit evidence. A stream of individual findings is not a structured test report, so most auditors will not accept it in place of a pentest.
However, none of these makes a bug bounty a bad idea. They make it a poor first step and a poor substitute for testing you must prove to an auditor.
Where Bug Bounties Win
A bug bounty adds real value once the basic gaps are closed. It does a few things better than any pentest:
- The testing never stops. A pentest is a snapshot. A bug bounty keeps running as your product changes.
- More minds look. Hundreds of researchers bring techniques that a single pentest team may not have.
- You pay for results. Money goes to valid findings, not to hours.
- Missed issues still surface. Issues that appear after a pentest, or that the testers missed, can still be found and reported.
For this reason, mature companies with large, public-facing products often run both. The pentest proves coverage and satisfies auditors. The bug bounty keeps new testers looking at the product between tests. For a closer look at how manual and automated testing fit alongside both, see this comparison of automated and manual pentesting.
Book Your Free Cybersecurity Consultation Today!
The Missing Layer: A Vulnerability Disclosure Policy
Before either a pentest or a bug bounty, every company with an internet presence should have a vulnerability disclosure policy. A VDP is a public statement that tells outsiders how to report a security issue, what you will do with the report, and that you will not take action against people who report in good faith.
A VDP pays no rewards. The policy simply gives well-meaning researchers a safe, clear channel.
A VDP is not a lesser bug bounty. The policy solves a different problem: what happens when someone finds a flaw you did not ask them to look for. Without one, that person may not know whom to contact, may post the issue publicly, or may never report it at all.
The international standard for handling such reports is ISO/IEC 29147. In the US, CISA’s Binding Operational Directive 20-01 required federal civilian agencies to publish one.
The 3 layers build on each other:
| Layer | What it does | Pays researchers? |
| Vulnerability disclosure policy | Gives outsiders a safe way to report issues | No |
| Bug bounty programme | Invites researchers to look, and pays for valid findings | Yes |
| Penetration test | Tests a defined scope in full, against a set method | No; you pay the testing team |
Kratikal runs a vulnerability disclosure programme service for companies that want this layer handled for them. This explainer on Kratikal’s VDP approach covers how it works.
Is a Bug Bounty Legal in India?
A bug bounty is legal in India when researchers stay within the programme’s terms, but the protection comes from the programme, not from the government. CERT-In’s disclosure and coordination policy says that reporting a vulnerability to CERT-In does not exempt the reporter from the law. The reporter remains responsible for how the vulnerability was found, and the policy sits under the IT Act, 2000.
As a result, the weight falls on your own programme terms. A bug bounty or VDP should state clearly what is in scope, which testing methods are allowed, and that you will not pursue legal action against researchers who follow the rules. Researchers outside those terms have no such protection. CERT-In itself coordinates disclosures between reporters and vendors, and aims to resolve issues within 120 days of first contacting the vendor.
This is general information, not legal advice. Have your legal team review programme terms before launch.
Which One Satisfies Compliance?
A pentest satisfies compliance requirements that a bug bounty usually cannot. PCI DSS requirement 11.4 calls for internal and external penetration testing to a documented methodology, at least every 12 months and after significant changes. The PCI Council’s PCI penetration testing guidance describes testing as essentially manual work against a defined scope, which a bug bounty does not provide.
SOC 2 and ISO 27001 auditors look for evidence that a capable, independent party tested the in-scope controls within the audit period. Bug bounty findings can support that evidence.
They rarely replace a pentest report, because they offer no set method, no full coverage, and no retest record. The case for that retest record is set out in remediation over reports. CERT-In audits and SEBI’s VAPT requirement go further: the testing must be done by a CERT-In empanelled auditor.
For the full picture by standard, see this guide on automated pentest compliance. The same logic that rules out automated-only testing also rules out bug bounty findings as a replacement for a pentest. This PCI DSS compliance guide covers the wider standard.
Which Do You Need? A Pentest vs Bug Bounty Path by Stage
The right answer to pentest vs bug bounty depends on where your security programme is today.
| Stage | What to run | Why |
| Early: first product, first audit | A vulnerability disclosure policy and a pentest | Closes the obvious gaps and gives auditors and customers a report |
| Growing: regular releases, more customers | Add continuous or more frequent pentests, and a private bug bounty | Keeps pace with change, and brings in invited researchers on a controlled scope |
| Mature: large public product, strong triage team | Add a public bug bounty and red teaming | Brings the widest pool of researchers, and tests detection and response |
Two rules hold at every stage. First, do not launch a bug bounty before a pentest has cleared the obvious issues, or researchers will collect payouts for flaws a pentest would have found for a fixed fee. Second, do not drop the pentest once a bug bounty is running, because the pentest is what proves coverage to auditors.
Continuous testing can bridge the gap between stages. Penetration testing as a service (PTaaS) runs manual tests on demand and keeps automated coverage between them. Read what PTaaS is for the model. Once both are in place, red teaming exercises test whether your team spots and stops a real attack.
Join our weekly newsletter and stay updated
Choosing Between a Pentest and a Bug Bounty
The bug bounty had been live for a year. Hundreds of reports, dozens of payouts, a healthy dashboard. But the internal admin panel had never been tested, because no researcher could reach it. That is the gap a pentest closes, and the reason the pentest vs bug bounty question is really about order, not choice.
Start with a vulnerability disclosure policy and a pentest. Then add a bug bounty when your product is large, public, and changing fast, and when you have the team to triage what it brings. Keep the pentest throughout, because it is the evidence auditors and customers ask for.
If you are planning that sequence now, Kratikal’s PTaaS testing services cover the testing layer with manual tests on demand and retests, and its VDP service gives researchers a safe way to report what they find. Kratikal is also CERT-In empanelled, which matters when Indian regulators set the rules.
FAQs
Buyers comparing a pentest with a bug bounty most often ask the questions answered here.
The difference between penetration testing and a bug bounty is coverage and accountability. A penetration test is a scoped engagement by a hired team that tests every item in scope against a methodology and delivers a report. A bug bounty pays outside researchers for each valid finding, with no promise about what they test. Pentests prove coverage; bug bounties add ongoing, wide-ranging scrutiny.
Penetration testing and bug bounty are not the same, although both look for vulnerabilities. A penetration test is a contracted, time-boxed project with a defined scope, a methodology, and a formal report that auditors accept. A bug bounty is an open-ended programme that rewards researchers per finding. Most companies run a pentest first and add a bug bounty once their programme matures.
A bug bounty is legal when researchers follow the programme’s published scope and rules, and the company has authorised testing. Testing outside those terms can break computer misuse laws, such as India’s IT Act, 2000. CERT-In’s disclosure policy makes clear that reporting a vulnerability does not exempt a researcher from the law, so clear programme terms and safe harbour language matter.
Bug bounty is still relevant for companies with large, public-facing products and the team to handle a steady flow of reports. It adds continuous scrutiny and a wide pool of skills that no single pentest team can match. It is not a replacement for pentesting, though, because it offers no coverage guarantee and little audit evidence.
The difference between a vulnerability disclosure program and a bug bounty is payment and invitation. A vulnerability disclosure program gives outsiders a safe, clear way to report security issues they find, and pays no rewards. A bug bounty actively invites researchers to look for vulnerabilities and pays for each valid finding. Every company should have a disclosure programme; a bug bounty comes later.