IoT devices have supported our homes, factories, healthcare systems, businesses, and our critical infrastructure. There are now smart cameras, advanced sensors, and other devices that rely on software and connectivity. While the software and connectivity allow IoT devices to be useful and convenient, they also increase the number of attack vectors. It is crucial to identify and test IoT attack vectors during device development. An attack vector can be hidden in an interface, firmware, communication channel, or service.
If attackers discover a vector after release, the manufacturer may need to issue an emergency patch, manage operational disruptions, and address the resulting impact on customer, legal, and business relationships. NIST’s update to IR 8259 in April 2026 outlines cybersecurity tasks to be performed by IoT device manufacturers and outlines steps to be taken throughout the device’s lifecycle. This further validates the approach of integrating security into device development as opposed to adding it on at the end.
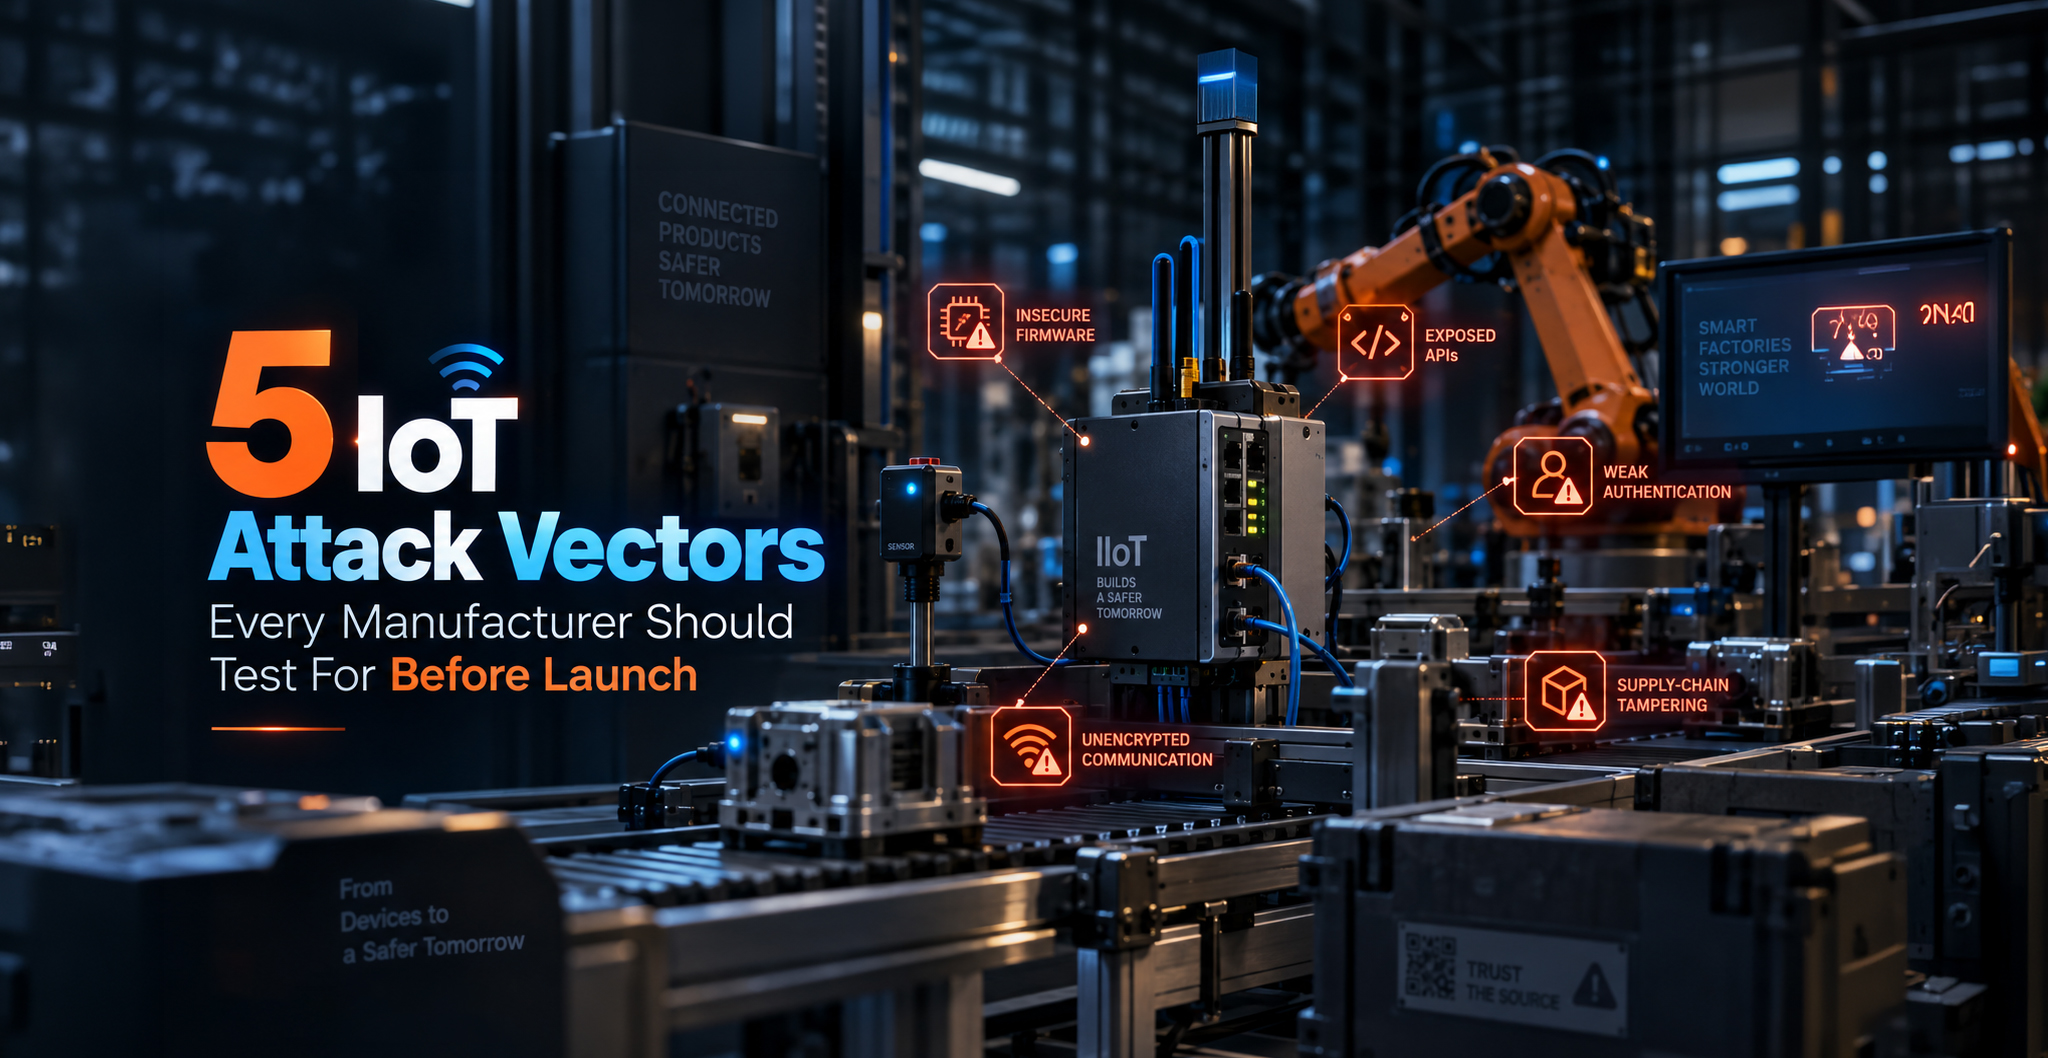
Manufacturers should use IoT security testing to assess how attackers could target devices and their services. Tests should look for weaknesses in hardware and cloud services and consider how attacks may be chained together. This blog analyzes five key IoT attack vectors that manufacturers should evaluate before releasing an IoT device.
Importance of Evaluating IoT Attack Vectors
IoT devices combine multiple elements, including hardware, firmware, software, cloud services, and other connected devices. Security vulnerabilities in one component can affect other elements. Pre-release testing gives manufacturers an opportunity to locate major security gaps in IoT devices.
- Unauthorized device or account access
- Manipulation of device functions or commands
- Interception of sensitive communications
- Exploitation of vulnerable firmware or components
- Movement from a compromised device into connected systems
The Growing Need for Pre-Launch IoT Security Testing
The IoT Security Foundation’s 2025 research found that only 40.53% of global IoT manufacturers had a vulnerability disclosure mechanism. This allowed security researchers to report security issues directly. The finding highlights an important lesson for manufacturers. However, identifying them before launch is far less disruptive. It helps manufacturers address risks before thousands of devices reach customers.
A strong pre-launch testing process helps manufacturers identify weaknesses across:
- Device hardware
- Firmware
- Communication protocols
- Applications
- APIs
- Cloud infrastructure
Testing these areas together provides a more realistic view of the product’s security posture.
1. Weak Authentication and Credential Attacks
Attackers target controls such as authentication. Compromising a device can be as easy as using default credentials, typing in simple, predictable passwords, or attacking a session control with a hardcoded secret. Inconsistent authentication can also lead attackers to APIs, administrative ports, or mobile apps.
Before releasing a device, manufacturers should test the firmware to determine whether attackers can easily guess credentials or extract secrets. Additionally, manufacturers should evaluate authentication and session controls, along with the device’s password reset and account recovery processes.
- Default usernames and passwords are removed or changed.
- Credentials are stored securely and cannot be recovered from exposed firmware.
- Rate limiting or other controls reduce brute-force attempts.
- Administrative functions require appropriate authentication and authorization.
- Sessions cannot be easily hijacked or reused.
2. Insecure Firmware and Software Exploitation
Firmware controls important device functions and can provide attackers with deep access when it contains security weaknesses. Outdated components, known vulnerabilities, hardcoded credentials, exposed debugging functions, and weak update mechanisms can all create attack paths.
Attacks can also be viable during an update; an attacker can modify a firmware image and distribute it to the devices. Testing should evaluate the update process.
- Firmware integrity and authenticity are validated.
- Updates use appropriate signing and verification mechanisms.
- Rollback or downgrade attacks are restricted.
- Devices do not expose unnecessary debugging interfaces.
- Known vulnerable components are identified and addressed.
3. Insecure Network Communication and Protocol Attacks
IoT devices use wired and wireless connections to communicate with applications, cloud services, gateways, and other devices. Poor encryption, weaknesses in TLS, insecure wireless configurations, open ports, and unsafe protocols can make these communications vulnerable to interception and manipulation.
Attackers can capture credentials, read or write sensitive data, alter commands, or direct the device to a malicious service. To realistically evaluate the security of device communications, IoT security testing must simulate attacks on device-to-device and device-to-cloud communications.
- Encryption of sensitive data in transit.
- Certificate validation and TLS configuration.
- Open ports, services, and unnecessary network exposure.
- Security of relevant Wi-Fi, Bluetooth, or other wireless protocols.
- Resistance to traffic interception and packet manipulation.
4. Vulnerable APIs and Cloud Interface Attacks
Many modern IoT devices use cloud services and API for the management and integration of devices, user authentication, and data processing. Compromising a secure device is possible if the backend services of the device have unsecured or over-privileged endpoints.
Testing should evaluate whether there are broken or compromised authentication/authorization mechanisms, excess data is exposed, endpoints are compromised, or injection attacks are possible. Cloud misconfigurations should also be assessed. For example, an API that lacks ownership verification could allow a user to access another user’s device or data.
- Device-to-cloud APIs and mobile application APIs.
- Administrative portals and backend services.
- Cloud storage and databases.
- Authentication and authorization services.
- Access permissions and API rate controls.
5. Physical Access and Hardware Interface Attacks
Remote attacks are not the only concern. An attacker with physical access to a production device may target JTAG, UART, USB, memory chips, debug ports, or removable storage. Exposed interfaces can allow firmware extraction, credential recovery, or other forms of privileged access.
Physical security testing should determine whether production devices expose unnecessary interfaces and whether sensitive information can be extracted through hardware access. Manufacturers should also verify secure boot, protected storage, and tamper-related controls where appropriate.
- Debug interfaces are disabled or adequately protected in IoT.
- Sensitive credentials and keys are securely stored.
- Firmware extraction is appropriately restricted.
- Secure boot mechanisms work as intended.
- Hardware ports do not provide unnecessary privileged access.
Book Your Free Cybersecurity Consultation Today!

How Can Manufacturers Build an Effective IoT Security Testing Process?
Security testing is more effective when it is built into device development rather than performed only immediately before release. NIST’s current IoT guidance covers cybersecurity activities before sale and throughout the device lifecycle.
Start early. Use security requirements and threat modeling during design so high-risk attack paths are identified before they become difficult to change. Test the complete ecosystem. Assess hardware, firmware, applications, APIs, networks, and cloud services together rather than treating each layer as isolated.
Repeat testing after major changes. Manufacturers should repeat security assessments whenever they introduce new firmware, features, integrations, or backend changes, as these updates can introduce new weaknesses. A clear process for receiving, assessing, and addressing reported vulnerabilities helps manufacturers respond after launch and before it.
Practical Checklist for Testing IoT Attack Vectors
- Authentication: Remove default credentials, protect stored secrets, and test brute-force resistance.
- Firmware: Check component vulnerabilities, signing, secure updates, and device debug controls.
- Network: Validate encryption, certificates, wireless security, and exposed services.
- APIs and cloud: Test authentication, authorization, data exposure, permissions, and configuration.
- Hardware: Consider debug ports, secure boot, storage, and firmware extraction.
How Can Kratikal Help You with IoT Device Security Testing?
Testing these IoT attack vectors before launch is essential for identifying weaknesses across the device, firmware, network, APIs, and other connected components. This is where Kratikal can help. Kratikal offers comprehensive IoT device security testing to identify and address vulnerabilities across IoT systems, helping organizations ensure robust protection against potential cyber threats.
Its expertise includes penetration testing, vulnerability assessments, and compliance checks, enabling organizations to safeguard sensitive data while maintaining secure and resilient IoT networks. With a thorough approach to IoT security testing, Kratikal helps organizations identify security gaps before attackers can exploit them. This enables manufacturers to strengthen their IoT products, reduce security risks, and operate with greater confidence in an increasingly connected world.
Join our weekly newsletter and stay updated
Conclusion
IoT devices consist of multiple layers, including hardware, embedded software, and services. Each layer has its own security concerns, and testing IoT devices should take a similar approach. Manufacturers should test their IoT devices against weak authentication, insecure firmware, vulnerable APIs, and unprotected hardware interfaces.
A methodical approach to testing IoT devices allows manufacturers to find and fix vulnerabilities before they become customer issues. Threat modeling, combined with testing of hardware and software, and APIs and networks, can help minimize the number of incidents a newly launched device encounters.
FAQs
- What are IoT attack vectors?
An attack vector in the Internet of Things (IoT) is a path or an approach that an attacker uses to breach an IoT device or to breach the ecosystem that the device is a part of. Weak or compromised credentials, vulnerabilities in firmware and APIs, unprotected hardware interfaces and unprotected communications are a few examples of attack vectors in IoT.
- Why is it important to test IoT devices before release?
Testing prior to release gives manufacturers the opportunity to find and fix vulnerabilities that otherwise may require an unexpected release to fix, potentially causing customer detriment and security incidents.
- What does IoT security testing include?
It can include hardware and firmware assessment, network and wireless testing, application and API testing, authentication reviews, cloud security checks and validation of update mechanisms.
- What differentiates testing for IoT security from regular penetration testing?
IoT security testing extends the attack surface to the device’s ecosystem, including embedded firmware and hardware, and wireless communications and physical attacks.
- What are the most prevalent attack vectors for IoT devices?
Weak or default authentication, insecure firmware, vulnerable network communications and APIs, cloud connections, and exposed hardware and debugging interfaces are just a few of the attack vectors for IoT devices.
- When do you think manufacturers should be doing IoT security testing?
It should start during the design and development process and continue to be done multiple times, including right before the launch and after any significant changes to the firmware, application, API, or infrastructure.
- Can firmware vulnerabilities pose a risk to an IoT device?
Yes, firmware vulnerabilities can allow attackers to steal secrets, change device behavior, and even infect the device with malicious code. The impact will depend on the firmware protection.
- How frequently should IoT devices be tested for security?
There is no single frequency that can be applied to all devices. Testing should be done prior to launch, and the security should be reevaluated after any significant changes are made to the device, firmware, software, or infrastructure. The manufacturer should also have a process to address newly discovered vulnerabilities.