Kratikal Blogs - Information Hub For Cyber Security Experts

Penetration Testing Frequency: How Often Should You Run a Penetration Test?

November 17, 2026 - 17 mins read

Penetration testing should be conducted regularly across all critical systems, with additional testing after significant changes. Systems that handle sensitive…
The Invisible Threat: Understanding the Hidden Risks of AWS Supply Chain Attacks

November 17, 2026 - 8 mins read

Compromised software dependencies can put an entire cloud environment at risk. Even when an organisation’s AWS infrastructure is secured with…

CISO’s AI Security Checklist OWASP LLM Top 10 Controls That Don’t Block Product Teams

November 16, 2026 - 8 mins read

Security leaders need to build security controls for AI-powered products quickly, and in a way that doesn’t stifle innovation. Traditionally,…

Do Automated Pentests Satisfy Auditors? A Compliance Guide

November 16, 2026 - 11 mins read

Automated pentests on their own rarely satisfy auditors. PCI DSS rules them out: the PCI Council’s guidance says running an…

Web Application Penetration Testing: Methodology, OWASP Coverage and Checklist

November 14, 2026 - 8 mins read

Web applications handle critical business operations, customer information, financial transactions, and sensitive organisational data. As businesses expand their digital presence,…

Autonomous Pentesting Platform (AutoSecT): Features, Capabilities and Evaluation Criteria

November 13, 2026 - 7 mins read

An autonomous pentesting platform uses AI agents to find, exploit and verify security weaknesses on its own, the way a…

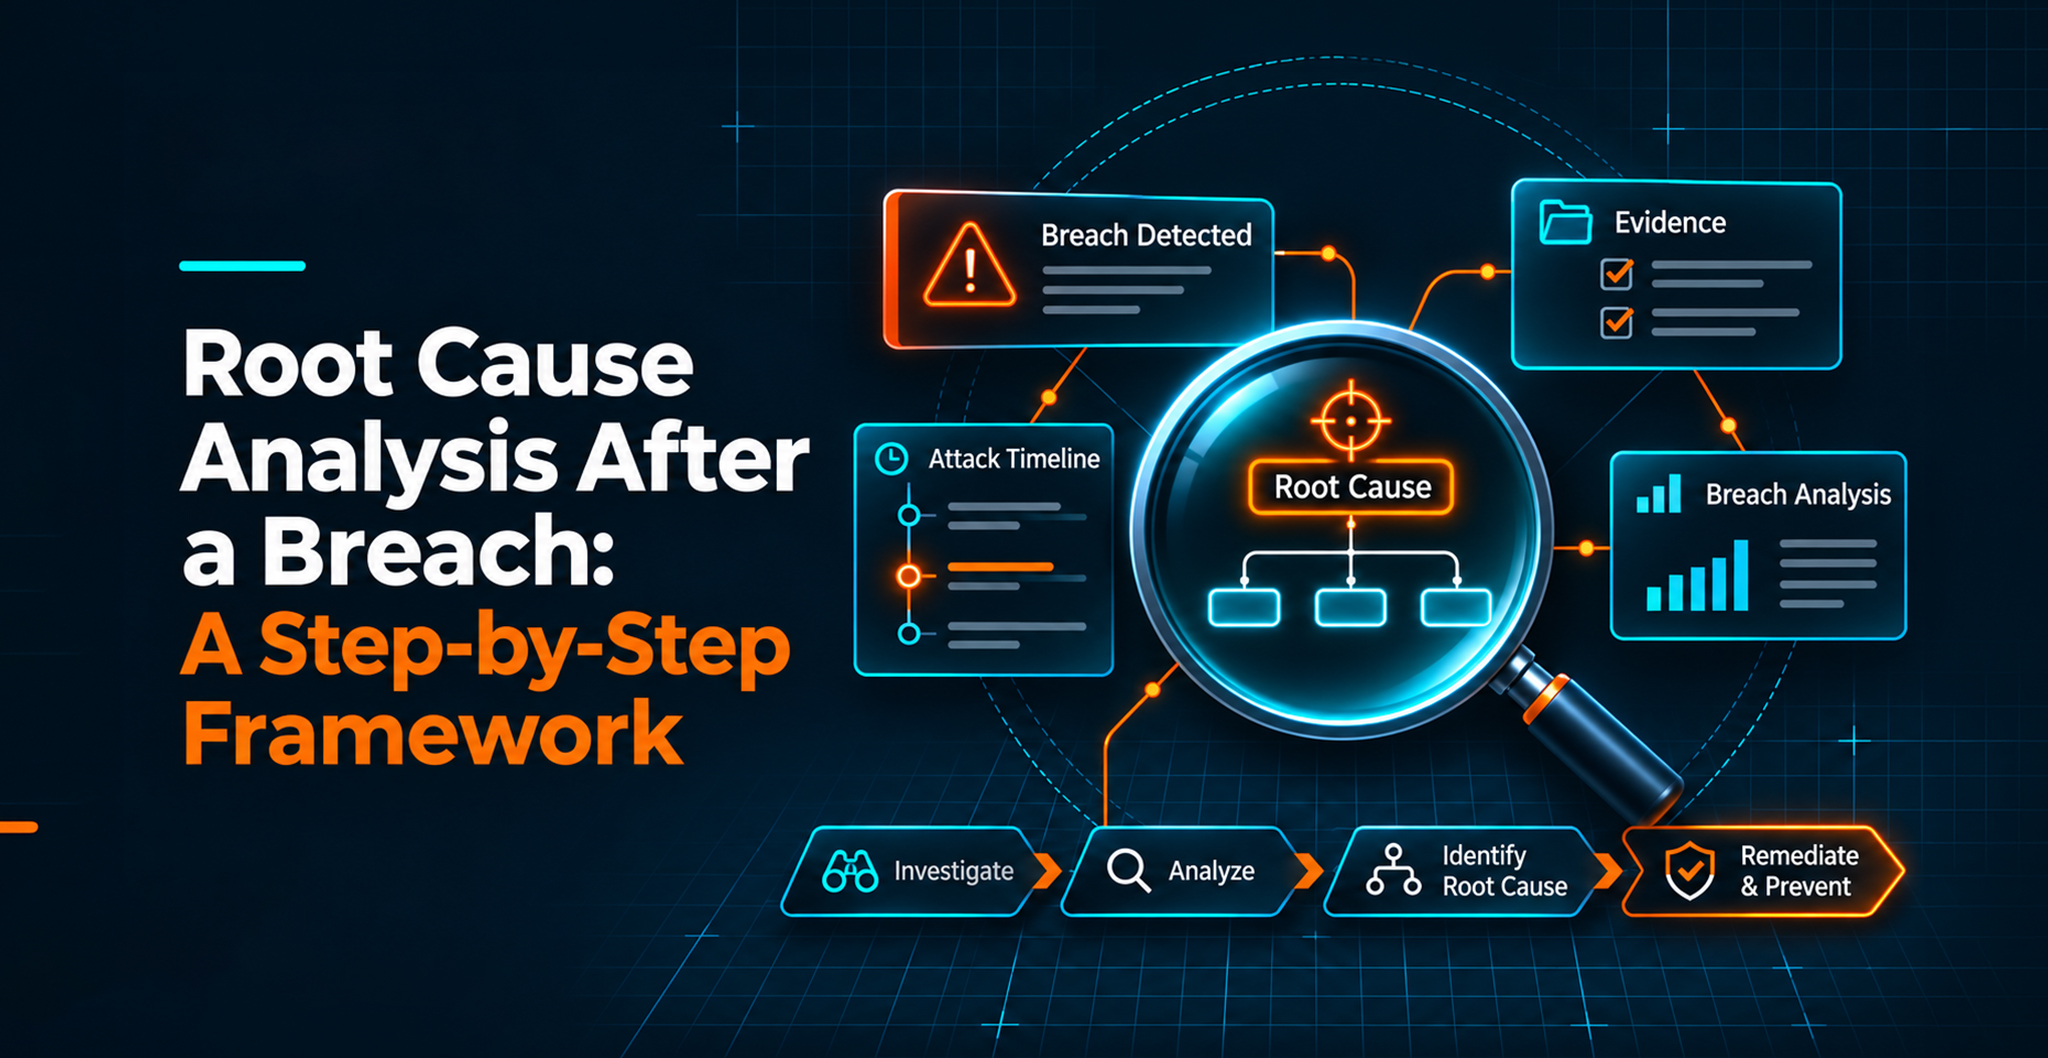
Root Cause Analysis After a Breach A Step-by-Step Framework

November 11, 2026 - 9 mins read

A data breach is more than just a security incident. Often, it is the first incident where attackers successfully exploit…

OAuth 2.0 Security Testing: Common Vulnerabilities in Authentication Flows

November 10, 2026 - 7 mins read

A successful login does not prove that an application’s identity and access controls are secure. Behind a “Sign in” button,…