Penetration Testing Frequency: How Often Should You Run a Penetration Test?
Penetration testing should be conducted regularly across all critical systems, with additional testing after significant changes. Systems that handle sensitive…
306 Articles
Penetration testing should be conducted regularly across all critical systems, with additional testing after significant changes. Systems that handle sensitive…
Automated pentests on their own rarely satisfy auditors. PCI DSS rules them out: the PCI Council’s guidance says running an…
Web applications handle critical business operations, customer information, financial transactions, and sensitive organisational data. As businesses expand their digital presence,…
A data breach is more than just a security incident. Often, it is the first incident where attackers successfully exploit…
A successful login does not prove that an application’s identity and access controls are secure. Behind a “Sign in” button,…
The advantage attackers once gained from speed is now being amplified by artificial intelligence. An AI agent can scan exposed…
Penetration testing takes a more hands-on approach. Skilled security professionals simulate real-world attack techniques to exploit identified weaknesses, uncover hidden…
Mobile apps handle banking transactions, health records, personal identities, and corporate data. All of those interactions travel over a network,…
GraphQL has changed how applications retrieve and consume data. Instead of exposing multiple endpoints for different resources, GraphQL typically provides…
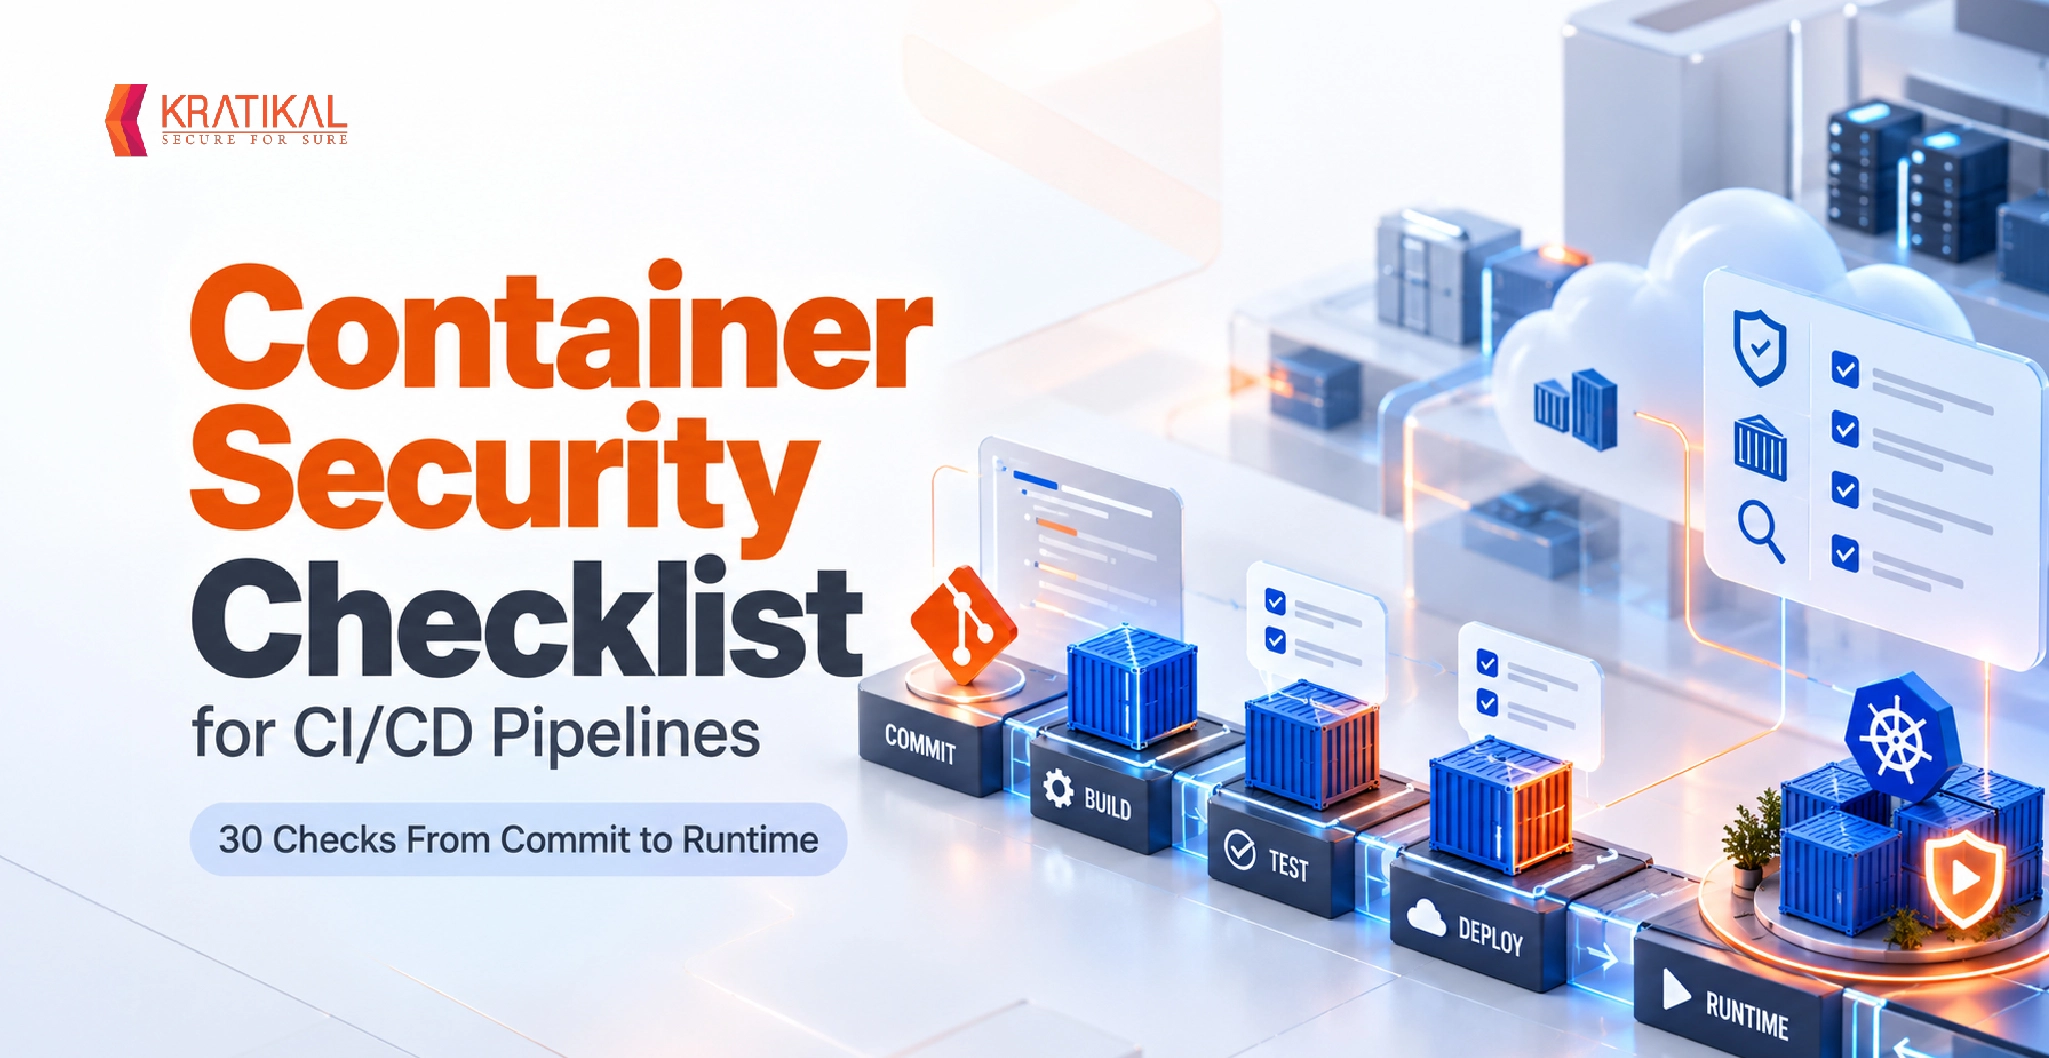
A container security checklist for CI/CD pipelines is a set of enforced checks that every container image must pass between…